
Digital Security is deeply tied to people, because the way the regulation of online behaviour and information security are defined and implemented has enormous implications for human rights, above all for privacy, freedom of expression and free association.
The Spanish Constitution and article 82 of Organic Law 3/2018 of 5 December on Personal Data Protection and the Guarantee of Digital Rights establish the right to privacy of communications, or secrecy of communications, whatever the channel through which they are transmitted. The law stresses in particular that “users have the right to the security of the communications they transmit and receive over the Internet”, and it also adds an obligation for service providers: the duty to “inform users of their rights”.
Digital Security is the central pillar of the New Digital Society. None of the strategies and policies being shaped today will make sense unless they exist in a context of Security with guarantees for the Human Being. But there is an enormous difficulty in finding a definition of what is meant by Digital Security that includes clear commitments to respect for human rights. This is complicated further when associated concepts and technologies quickly appear that add more confusion to the debate, such as cybercrime, cyberwar, cyberdefence, cyberattack, hacking, biohacking, ethical hacking, artificial intelligence, extended reality, cobotics, neuroimplants, captology, and a long list that means regulation experts cannot keep up with the dizzying pace of technological progress well enough to understand it and act accordingly.
However, despite the difficulty, everyone involved agrees that “Digital Security and human rights are complementary, mutually reinforcing and interdependent”. It is therefore an urgent necessity to recognise that the main goal of Digital Security must be the protection of people and, consequently, of human rights.
In this sense, the definition that best fits this concept from a Technohumanist approach would be the one set out by the Freedom Online Coalition, perhaps the most respectful of human rights: “Cybersecurity is the preservation, through policy, technology and education, of the availability, confidentiality and integrity of information and its underlying infrastructure so as to enhance the security of persons both online and offline”. This definition recognises the importance of respecting human rights both online and offline. It also considers the role of technological innovation as a driver for promoting the free flow of information in digital media. In this way, it reinforces the relationship between digital security and human rights in order to promote freedom and security.
The right to digital security
Given the definition of Digital Security adopted by the Technohumanist Movement, it is worth setting out a series of principles needed to ensure that both technologists and legislators can find common ground for establishing policies that secure and preserve people’s wellbeing in the face of technological progress and evolution.
- Replace the concept of cybersecurity with that of digital security, which goes beyond the military sphere and must be conceptually centred on the protection of citizens, individuals and their communities. Digital security must also serve to promote economic and social development on the basis of the principles of the rule of law and the protection of fundamental rights.
- Align any digital security strategy with the human rights legal frameworks of each country, of the inter-American system and of international standards such as those described in the International Principles on the Application of Human Rights to Communications Surveillance, giving particular weight to the protection and guarantee of the exercise of the rights to freedom of expression, to privacy and to free association.
- Adopt instruments and mechanisms of transparency and accountability, including Open Government plans, on the implementation and development of digital security strategies in each country that are measurable and verifiable.
- Recognise the importance of secure encryption as an element of digital security necessary for the protection of communications and data. Consequently, it is advisable that States promote and respect its wide use and development by citizens, companies and governments.
- Use risk analysis methodologies such as “privacy by design” and human rights impact assessment, to ground the formulation and implementation of evidence-based public digital security policies.
- Promote and encourage better, resilient and up-to-date computer systems that strengthen digital security. In this regard, it is advisable for these systems to be audited publicly and continuously, with their source code available without legal obstacles.
Ethical Hacking
Addressing the complex scenario of Digital Security inevitably means talking about Hacking and Hackers. Ethical Hackers are the professionals who devote themselves to preserving and consolidating the Security of Digital Systems. They are experts who specialise in penetration testing of computer systems and software in order to assess, strengthen and improve security. Their work consists mainly of “hacking” a system and identifying and fixing possible vulnerabilities, which effectively prevents exploitation by Dark Hackers or cybercriminals. This type of Hacker is called a white hat Hacker (White Hat), to distinguish them from the cybercriminal Hackers, who are known as black hat Hackers (Black Hat).
Most organisations believe that the act of authorising an Ethical Hacker to test a company’s defences is enough to guarantee legal protection and provide the necessary cover for the questionable activities that will be carried out. This depends on how far the hacker goes in the process of testing the systems, since at some point they may switch to grey hat mode (Gray Hat), where laws and the fundamental rights of people and their data could be violated.
For example, with the use of social engineering, a technique that tricks people into handing over confidential information. There is a thin line between using this technique ethically or maliciously. Ethical or white hat hackers would use it to help test a company’s defences, since under a real attack a black hat hacker would do the same. But ultimately, its mere use goes against the defence of human rights and the security context that one wants to preserve.
On certain occasions the Ethical Hacker ends up entering the systems using another person’s credentials, obtained by illicit methods. At this point laws are being broken, since they have access to confidential information. If it concerns customer or employee information, the hacker and the company may violate the various data protection laws in force. Companies need to test their security, which is obviously necessary, but by granting their permission they cover their corporate eyes and ears while these processes are carried out. As a final result, a detailed report is delivered pointing out the weaknesses and the recommendations to take into account. The controversy is that it is very likely that along the way laws have been broken that the professional himself does not know or does not care to acknowledge.
Biohacking
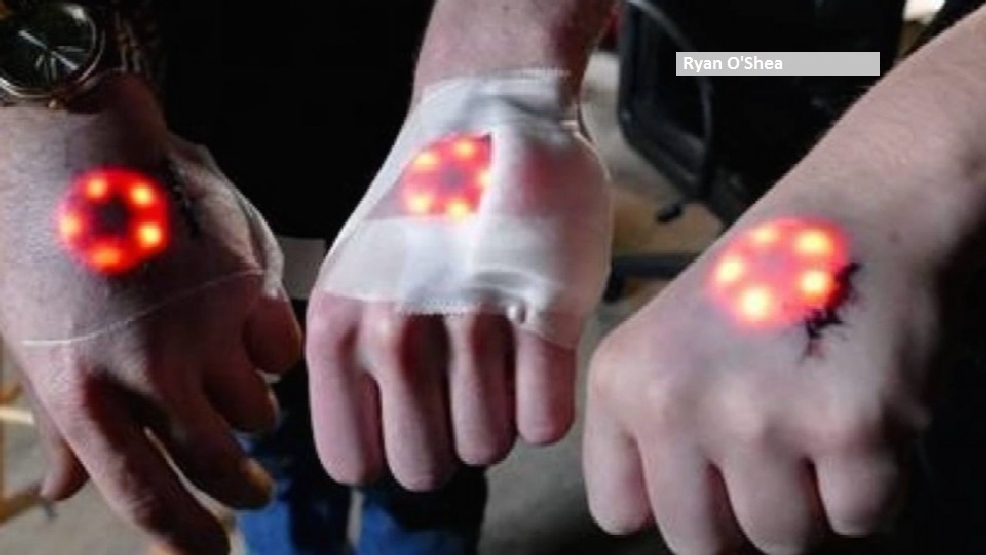
BioHacking has so far been presented to us with the maxim of optimising health to the limit. That is the goal of Biohackers, whose motto upholds “Being the best version of yourself”. Just as Hackers push Digital Systems to the limit, Biohackers hack the human body using a multitude of devices and techniques to take Homo Sapiens to the next level, that of the Augmented Human Being, as the Transhumanist movement proclaims.
According to transhumanists, it is a mindset that aims to intervene in our own biology, and modify the properties of the brain and of consciousness. It consists of combining science and technology to measure different biological and psychological variables so as to apply certain interventions, or biohacks, and analyse their impact on the human being. For this movement, an open mind and a proactive attitude are indispensable requirements for finding what works in what they call one’s own neuroindividuality, and for achieving a quantified self that allows one to take control of both the internal and external environment, and thus optimise biological and mental variables quickly and measurably.
Each of the emerging technologies of the Fourth Industrial Revolution generates an ethical debate that is still in its early stages. If Digital Security and the Hacking of Systems already pose a major challenge that is hard to face, the next frontier is not even visible on the horizon. The problem BioHackers do not talk about is the enormous exposure to cyberattacks that a bio-implanted person would have, or simply one exposed to a multitude of Internet of Everything devices that handle a huge amount of sensitive and personal data, such as heart coherence, for example.
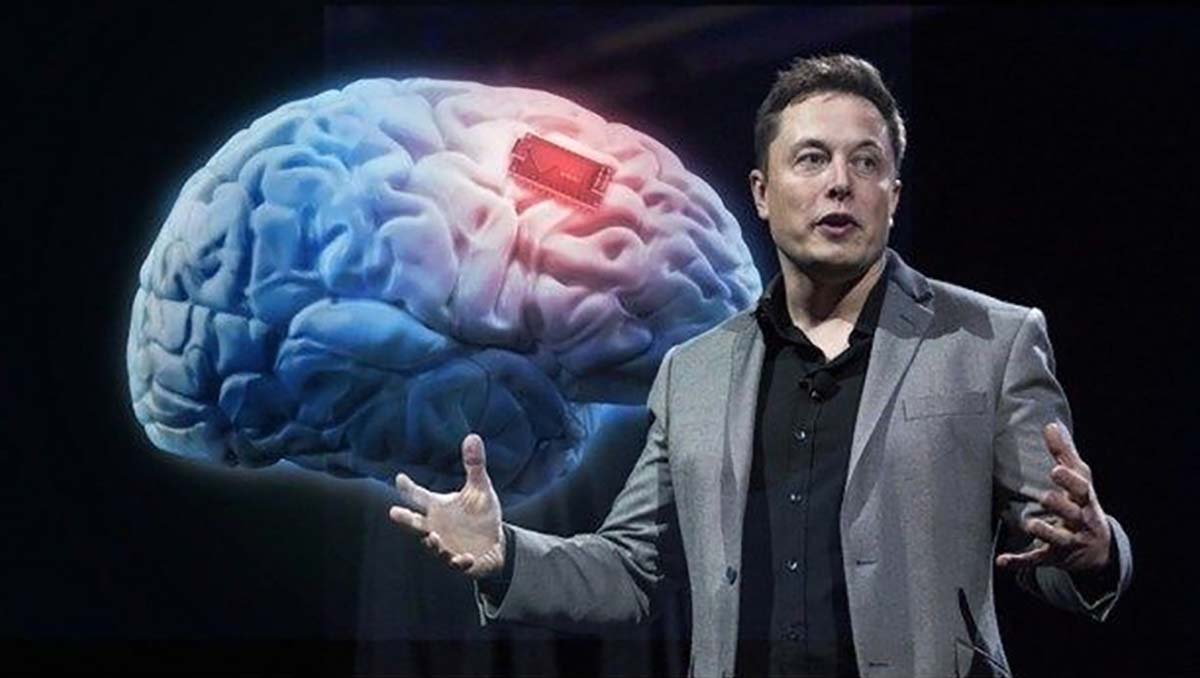
When thought and consciousness are exposed to cybercrime or cyberwar through hyperconnected digital systems with artificial intelligence capabilities, which will live inside our body like the Neuralink neuroimplants of Elon Musk, the importance of Security and of preserving human rights will become crucial. The augmented human will need strong legislation to protect them if we truly want to build a real Techno-Anthropocentric future.
Originally published in Spanish on IANética (2020). English version prepared for TecnoHumanismo.
Related articles
The Right to Control Your Data: Our Data Belongs to Us
The Right to Data Control. A Fundamental Right over the Control of Personal Data will be one of the basic pillars of the Second Renaissance.
Read article →6 min
RTVE Informe Semanal: Our Technohumanist View on the Report «Rumbo al Metaverso» (Heading for the Metaverse)
A 15-minute report aired nationwide on La 1 and the 24 Horas channel on 4 June 2022. Pedro Mujica opens by defining the Metaverse.
Read article →3 min
Ethics of Advanced Robotics and Humanoids
As advanced robotics and humanoids take hold, an essential debate on ethics emerges: how to integrate AI into robots while protecting human dignity.
Read article →6 min